HIPAA for Gyms: What Triggers Coverage and Fixes in 30–90 Days
Most U.S. gyms are not covered by HIPAA. The exceptions matter, though: you likely fall under HIPAA if your facility bills health plans electronically for clinical services, runs an on-site physical therapy or occupational therapy operation, or handles eligibility and outcome data for an employer’s group health plan as a business associate. If none of those describe you, HIPAA probably doesn’t apply, but state privacy laws might. Map your data flows against the scenarios below before you assume either way.
TL;DR:
- Gyms only fall under HIPAA if they bill insurance, provide clinical services, or handle PHI on behalf of covered entities and business associates.
- Handling diagnosis codes, insurance claims, or contracted clinicians’ notes introduces PHI and activates HIPAA compliance obligations.
- Once HIPAA applies, gyms must conduct risk analyses, implement safeguards, and establish clear vendor BAAs to protect electronic PHI effectively.
- Most gyms do not need extensive HIPAA compliance unless they significantly expand into clinical or employer wellness services, where state laws may also impose privacy requirements.
- Consolidating operations with specialized clinical platforms and reducing vendor variety can minimize compliance complexity and risk exposure.
Getfitnessflow
Simplify Your Gym Operations
Fitness Flow brings scheduling, billing, sales, and member engagement together, helping gyms reduce vendor sprawl and administrative workload.
Table of Contents
- HIPAA for Gyms: When Does It Actually Kick In?
- PHI, Covered Entities, and Business Associates: The Terms You Need Straight
- If HIPAA Applies, Here’s Your Compliance Roadmap
- Contracts and BAAs: Controlling Your Vendor Exposure
- When HIPAA Doesn’t Apply, State Law Often Does
- Your HIPAA Compliance Checklist: This Week, This Quarter, This Year
- The Real Trade-Off: Build for HIPAA or Keep Clinical Data Separate
- Simplify Your Gym’s Operations Without the Vendor Sprawl
- Sources
- FAQ
HIPAA for Gyms: When Does It Actually Kick In?
HIPAA was written for healthcare providers, health plans, and their vendors, not fitness businesses. A gym crosses into HIPAA territory the moment it starts acting like one of those three roles, usually without realizing it happened.
Here’s where that line actually gets crossed in real gyms:
- On-site clinical services that bill insurance. If you run a physical therapy suite, offer occupational therapy, or administer vaccinations and submit electronic claims to a health plan, you meet the CMS standard for a covered entity conducting standard electronic transactions.
- Employer wellness programs tied to a group health plan. When an employer’s health plan sends you eligibility data, biometric screening results, or outcome reports to run a corporate wellness program, you’re handling that plan’s protected data as a business associate, even though your gym itself isn’t the plan.
- Vendors and independent clinicians touching PHI on your behalf. A contracted physical therapist billing through your facility, or a third-party biometric screening company reporting results back to an employer plan, can pull your gym into HIPAA’s reach even if you never touch a claims form yourself.
- EHR integrations, remote monitoring, or telehealth run from your facility. If you’ve added remote patient monitoring, telehealth visits, or an electronic health record integration, you’ve built infrastructure that handles the exact kind of data HIPAA regulates.
Most boutique studios, big-box gyms, and CrossFit affiliates never touch any of this. The risk shows up when a gym adds a “medical fitness” angle, partners with a corporate wellness client, or brings in a clinician to expand services, often without updating contracts or data handling to match.
PHI, Covered Entities, and Business Associates: The Terms You Need Straight
Protected Health Information (PHI) is individually identifiable health information tied to treatment, payment, or health care operations, according to HHS’s definition. A name attached to a diagnosis, a treatment note, or an insurance claim is PHI. A member’s attendance log or a generic “completed 45 minutes on the treadmill” workout entry is not.
Covered entities are health plans, health care providers who conduct standard electronic transactions (claims, eligibility checks, billing), and health care clearinghouses. Business associates are vendors or contractors who perform a function involving PHI on a covered entity’s behalf, think billing software vendors, cloud hosts storing claims data, or a screening company reporting results to an employer plan.
For gyms, the line is data type, not intent. A member’s squat max and check-in history stay outside HIPAA. A diagnosis code, an insurance claim number, or a note from a contracted physical therapist crosses into PHI the moment it’s tied to an identifiable person.
If HIPAA Applies, Here’s Your Compliance Roadmap
Once you’ve confirmed HIPAA applies, don’t try to tackle everything at once. Work through it in this order:
- Run a documented risk analysis first. Map every place electronic PHI (ePHI) lives, who can access it, and where it moves, this is the foundation every other safeguard builds on.
- Put administrative controls in place. Appoint a privacy officer and a security officer (can be the same person in a small operation), write policies for minimum-necessary access, and train every employee who might touch PHI.
- Lock down physical access. Clinical areas need to be separated from the gym floor, workstations displaying PHI need privacy screens or positioning away from public view, and old devices or paper records need documented, secure disposal.
- Build technical safeguards. Encrypt ePHI at rest and in transit, require multi-factor authentication, assign unique login IDs to every user, keep audit logs, and use secure messaging instead of regular text or email for anything containing PHI.
- Prepare your breach response before you need it. Know your triage steps, your notification timelines, and the basics of reporting to the HHS Office for Civil Rights, because ransomware and other breaches move faster than ad hoc planning can handle.
Pro Tip: Run the risk analysis before you buy new software. Fixing a vendor contract after a breach is far more expensive than screening it beforehand.
The safeguards above map directly onto HIPAA’s Security Rule categories: administrative, physical, and technical. Skipping the risk analysis to jump straight to buying encryption tools is the most common mistake gyms make when they discover they’re in scope.
Contracts and BAAs: Controlling Your Vendor Exposure
A Business Associate Agreement (BAA) is required any time a vendor creates, receives, maintains, or transmits PHI on your behalf. That includes cloud hosting providers, EHR systems, billing companies, and analytics platforms that touch clinical data, not your general CRM or scheduling software, unless that system stores PHI too.
Before signing anything, check your contracts for:
- Breach reporting timelines and obligations, spelled out in specific days, not vague language.
- Security requirements the vendor commits to, not just a promise to “follow HIPAA.”
- Subcontractor flow-down clauses, so your vendor’s vendors are bound too.
- Clear terms for returning or destroying PHI when the contract ends.
Ask new vendors for a SOC 2 report or a completed security questionnaire before signing, and re-check existing vendors annually. If you use independent contractors or clinicians on-site, put their data-handling role in writing, even a one-page addendum closes a surprising number of gaps.
When HIPAA Doesn’t Apply, State Law Often Does
Most gyms that skip HIPAA entirely still face real privacy exposure through state law. Illinois’ Biometric Information Privacy Act (BIPA) and similar laws in other states regulate fingerprint and face-recognition check-in systems directly, and California’s CCPA/CPRA gives consumers rights over data your membership app or wearable integration collects.
Biometric check-in kiosks, keycard access logs, and location data from a branded app can all trigger liability that has nothing to do with HIPAA. In several BIPA cases, plaintiffs’ litigation costs have outpaced what a HIPAA breach would have cost the same business. The fix is unglamorous but effective: use clear consent forms before collecting biometric data, set retention limits so you’re not holding old fingerprint templates indefinitely, and keep your privacy policy specific about what you collect and why.
Your HIPAA Compliance Checklist: This Week, This Quarter, This Year
Spreading this out keeps it from becoming a project nobody finishes. Break it into three timeframes:
- This week: Answer the self-check questions from this article, inventory every vendor that touches member or clinical data, request BAAs from any vendor that qualifies, and implement multi-factor authentication and encryption as needed.
- Next 30 to 90 days: Assign a privacy officer, complete your formal risk analysis, implement the technical safeguards you’re missing, and update your intake forms and privacy notices to reflect actual practice.
- Every year after that: Test your breach response plan with a tabletop exercise, re-run the risk analysis after any new software or service launch, and refresh both staff training and vendor BAAs.
Pro Tip: Put a recurring calendar reminder on your risk analysis. Compliance done once and forgotten is the single biggest reason gyms get caught flat during an audit.
The Real Trade-Off: Build for HIPAA or Keep Clinical Data Separate
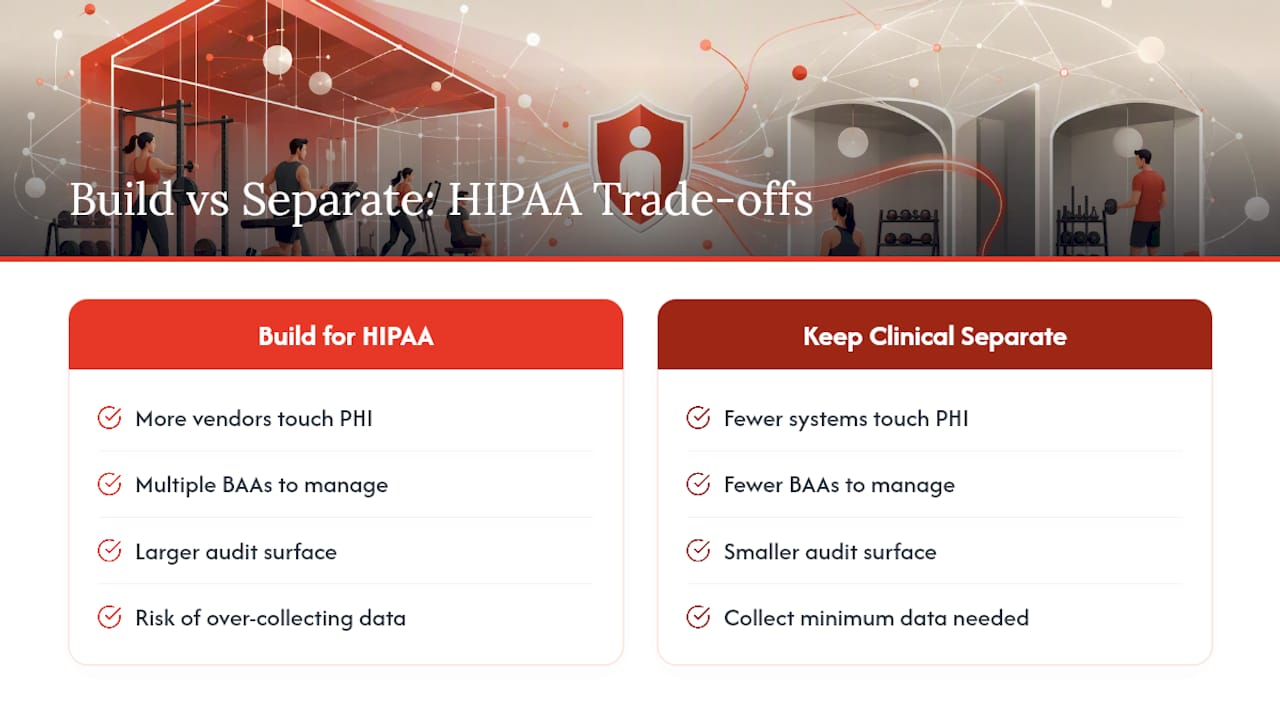
Most gym owners overbuild for compliance they don’t need, or underbuild for compliance they do. The smarter move is usually to keep clinical operations, and the vendors attached to them, walled off from your general membership systems entirely. Fewer systems touching PHI means fewer BAAs to manage and a smaller audit surface. Platforms like Fitness Flow help here simply by consolidating scheduling, billing, and member engagement into one system instead of five, which cuts down how many vendors could ever touch sensitive data in the first place.
If clinical services are a real part of your business, don’t try to retrofit general gym software into a HIPAA-ready clinical system. Partner with a specialized clinical platform for that piece, and keep your day-to-day gym operations, the stuff that has nothing to do with PHI, on a separate, simpler system. Collect the minimum data you actually need, contractually, and by default.
— Louis
Simplify Your Gym’s Operations Without the Vendor Sprawl
Fitness Flow is the alternative to juggling five disconnected tools for scheduling, billing, and member communication, every extra vendor is another potential point of PHI exposure and another contract to track. Consolidating those workflows into one platform doesn’t just save a significant amount of time in administrative work; it shrinks the list of vendors you’d need a BAA from in the first place.
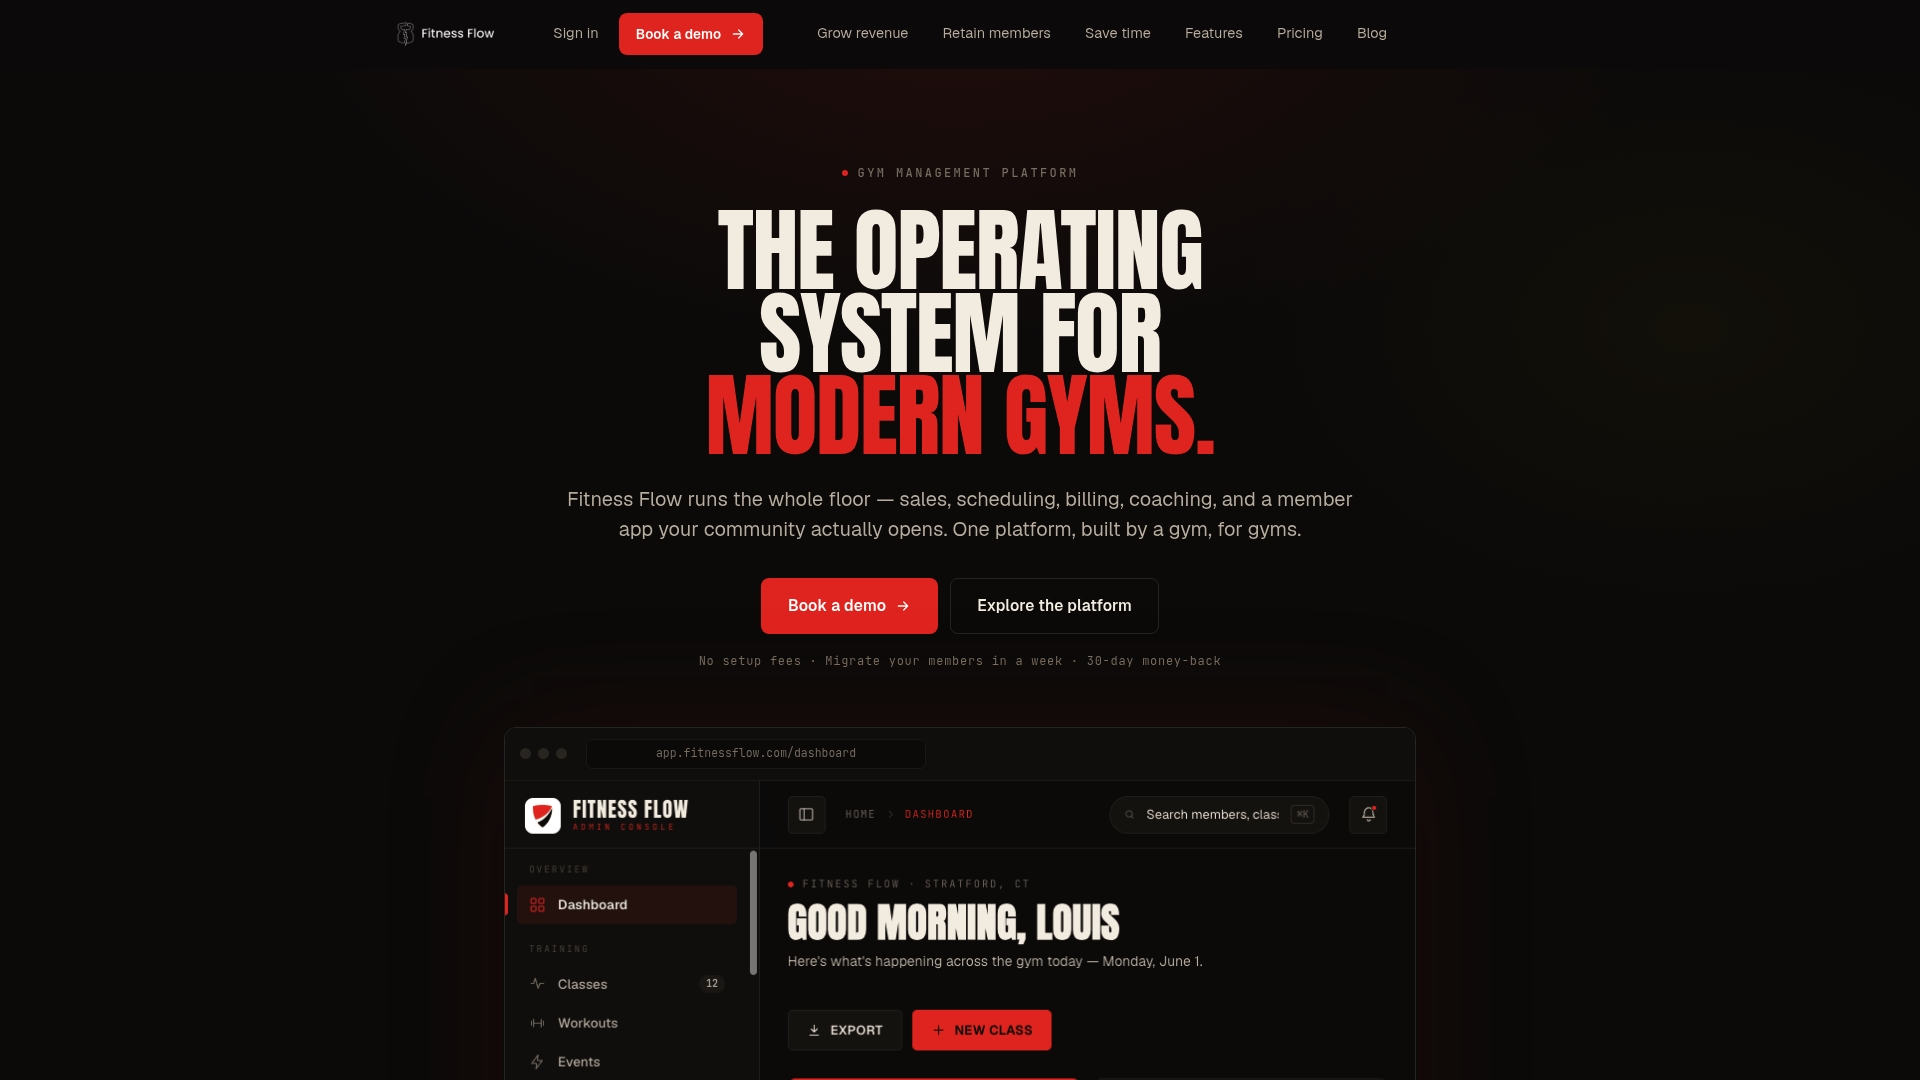
The platform’s unified member data controls and branded app mean fewer third parties touching sensitive information, and fewer systems to audit when you’re mapping your risk analysis. Whether you run a single studio or manage multiple locations, the Solo, Studio, or Multi-site plans scale with you, starting at a competitive monthly price for Solo and Studio plans. If you’re also working on visibility alongside operations, a partner like gym-focused SEO services can help fill your classes while your back office runs cleaner. Get a demo through the Fitness Flow site to see how consolidation looks for your specific setup.
This article is general information, not a substitute for advice from a qualified lawyer. Consult a qualified legal professional about your own circumstances before acting on anything here.
Sources
FAQ
Does HIPAA Apply to Personal Trainers?
Independent personal trainers generally aren’t covered entities under HIPAA, since they don’t bill health plans or conduct standard electronic transactions. If a trainer works within a clinical program that does bill insurance or handles employer wellness plan data, they can become a business associate subject to the same PHI rules as the facility itself.
What Counts as a HIPAA Violation for a Gym That Is Covered?
Common violations include failing to sign a Business Associate Agreement with a vendor that handles PHI, storing unencrypted health data, skipping a required risk analysis, missing breach notification deadlines, and letting staff access more health information than their role requires. Each of these ties back to gaps in the administrative, physical, or technical safeguards covered above.
What Is the Current HIPAA Rule Gyms Should Watch For?
HIPAA’s core structure, the Privacy Rule, the Security Rule, and the Breach Notification Rule, hasn’t changed for gyms specifically, but HHS continues to update guidance on ransomware response and ePHI protection as threats evolve. Gyms operating clinical or wellness-plan services should check HHS’s site periodically rather than assume last year’s guidance still covers every scenario.
What Are the HIPAA Laws in the USA in Plain Terms?
HIPAA sets national rules for how covered entities and their business associates protect health information, built around three main rules: privacy protections for PHI, security requirements for electronic PHI, and breach notification obligations when something goes wrong. It applies to health plans, most health care providers, and clearinghouses, plus the vendors that work with them, not to businesses outside those categories.
Is Consumer Fitness App Data the Same as PHI?
No. Data from wearables and consumer fitness apps generally isn’t PHI unless it flows through a HIPAA-covered entity or business associate relationship. That kind of data typically falls under FTC oversight and state consumer privacy laws instead, which carry different rules but real enforcement risk of their own.